Password security remains a core business control because stolen or reused credentials can give attackers access to email, cloud services and sensitive data.
The Cyber Security Breaches Survey 2025/26 found that 43% of UK businesses identified a cyber security breach or attack in the previous 12 months. Phishing, which frequently targets login details, affected 38% of businesses. The National Cyber Security Centre (NCSC) Annual Review 2025 records 429 incidents requiring NCSC support between 1 September 2024 and 31 August 2025. Of these, 204 were nationally significant.
This article explains how organisations can reduce credential risk using stronger password practices, multi-factor authentication (MFA), passkeys and password managers.
Passwords are no longer the only way to authenticate, but many business systems still rely on them. A password should therefore be treated as one layer in a wider identity and access control system, rather than as a complete defence.
Password security is essential for these reasons:
- Weak or reused passwords can create a route into multiple accounts. The Cyber Security Breaches Survey 2025/26 commissioned by the Department for Science, Innovation and Technology (DSIT) and the Home Office found that 74% of businesses had a policy requiring strong passwords, leaving around one in four without that basic control (DSIT, 2026).
- Cyber incidents can be disruptive and expensive. DSIT no longer reports a mean breach cost because costs are highly skewed. Among businesses whose most disruptive breach had an outcome, the median perceived cost was £560, and the 95th-percentile estimate was £15,000 (DSIT, 2026).
- Phishing remains the most prevalent type of breach or attack. It was experienced by 38% of all businesses and by 88% of businesses that identified any breach or attack. A convincing sign-in or password-reset lure can expose credentials even when the password itself is strong (DSIT, 2026).
- Organisations must protect personal data. The UK GDPR and Data Protection Act 2018 require appropriate technical and organisational security measures. They do not prescribe a particular password format, but password controls must be appropriate to the risk. The higher maximum fine is £17.5 million or, for an undertaking, 4% of total worldwide annual turnover in the preceding financial year, whichever is higher (ICO guidance).
A written cyber security policy should document the organisation’s rules for passwords, MFA, passkeys, account recovery, access reviews and incident reporting.
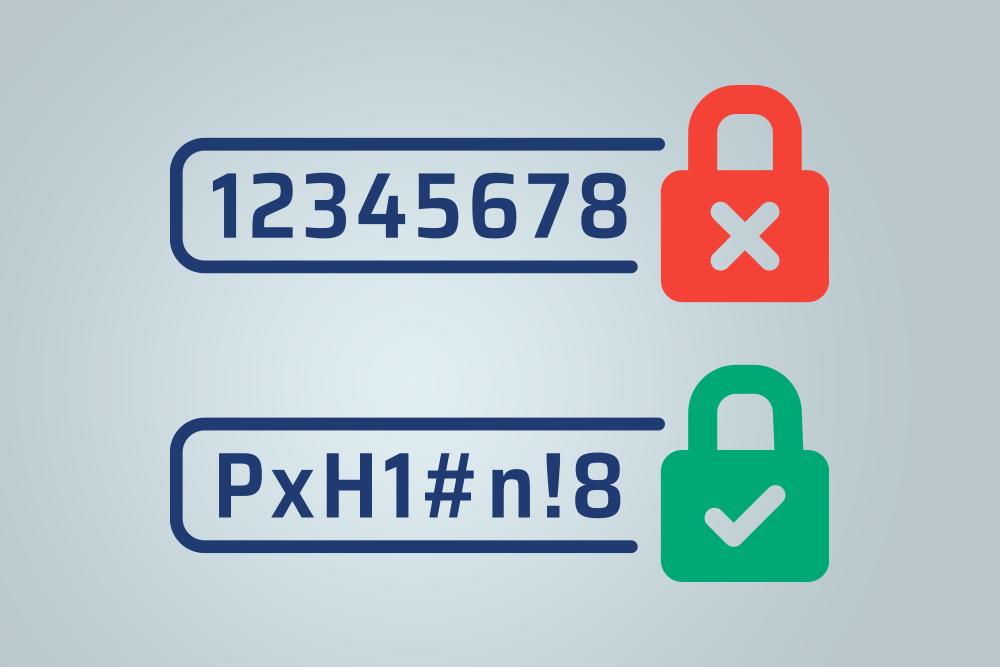
Many people choose passwords that are easy to remember, but predictable patterns and reused credentials are also easier for attackers to exploit. When a service still requires a password, prioritise length, uniqueness and unpredictability rather than relying on cosmetic complexity.
A weak password is usually a short, familiar word or a set of numbers. Examples of weak passwords include:
- The names of family members or pets
- Surnames with dates of birth (such as ‘surname1982’)
- Obvious words or sets of numbers (such as ‘admin’, ‘password’ or ‘password123’)
- Anything that is predictable or could be easily guessed
Where a passkey is unavailable, the NCSC recommends using a strong password, such as one generated by a password manager, and enabling two-step verification. If a password must be memorable, the NCSC’s three random words approach is safer than a familiar word with predictable numbers or character substitutions.
Use a different password for every service. Prioritise email, business banking, cloud administration and remote access accounts because compromise of one of these accounts may allow an attacker to reset passwords or reach other systems.
Organisations that configure password systems should allow long passwords, screen out common or breached passwords and avoid routine forced changes unless compromise is suspected. The ICO’s password guidance also recommends suitable password hashing, rate limiting and secure reset processes.
AI does not make a long, randomly generated password instantly crackable. Its near-term value to attackers is that it can improve the scale and targeting of existing techniques. The NCSC places social engineering, phishing and password attacks among the areas receiving an AI-related capability uplift, with a significant uplift for less-skilled actors (NCSC, 2024). Generative AI can also make credential-stealing messages and password-reset requests more convincing.
This development makes reused and predictable passwords more exposed. Unique generated passwords, passkeys and phishing-resistant MFA reduce the value of AI-assisted guessing and credential theft.
Maintaining optimum password security means taking measures to protect your passwords actively. There is no point in having a secure password if you leave it where someone can see it.
Follow these rules to make sure you always keep your passwords protected.
Use a unique password for every account so that a breach of one service does not expose other accounts. A password manager can generate and store these credentials.
Only 47% of businesses required two-factor authentication in 2025/26, although this was up from 40% the previous year (DSIT, 2026). The NCSC advises that password-only authentication is not strong enough for online services holding sensitive data and that organisations should use the strongest available MFA.
The NCSC recommends MFA methods in this order of preference:
- Passkeys and other FIDO2 credentials: These use public-key cryptography and resist phishing. When the trusted device also requires a PIN or biometric check, FIDO2 can provide strong passwordless MFA. The NCSC now recommends choosing passkeys over passwords wherever they are available.
- Challenge-based authenticator apps: Number matching and similar challenges are stronger than a simple approve or deny prompt. Users should check the sign-in details and reject unexpected requests because repeated prompts can be used in MFA fatigue attacks.
- Authenticator app codes: Time-based one-time codes are stronger than a password alone, but an attacker can still capture a code through a convincing phishing site.
- Hardware-based code generators: These are useful where mobile apps are unsuitable, although attackers can still capture one-time codes through phishing, and physical tokens require careful management.
- SMS, email or call-based codes: These provide additional protection, but the NCSC recommends using them only when stronger methods are not available (NCSC MFA guidance).
MFA should cover every user who can access sensitive data, especially administrators, remote access accounts and senior staff. Organisations should also protect account-recovery methods and ensure that legacy protocols cannot bypass MFA.
Do not share passwords by email, messaging apps or other unprotected channels. Where colleagues need access to the same service, use named accounts, delegated access or an approved password manager with controlled sharing and audit records. Do not type a password where another person can observe it.
Check the website address before entering credentials and treat unsolicited password-reset messages with caution. If a message claims that urgent action is required, open the relevant service directly instead of following its link. Keep devices and software updated, avoid entering work credentials on devices or networks that the organisation does not control and report suspected phishing promptly.
A password manager can generate and store a different strong password for every account. Current NCSC guidance does not advise against browser-based storage as a blanket rule. Its password manager guidance says that a manager supplied by a browser or device manufacturer can be suitable when convenience is the priority. A reputable third-party manager may be more appropriate when an organisation needs cross-platform support, managed sharing or additional administrative features.
When selecting a password manager for business use, assess the provider’s security track record, encryption, account-recovery controls, MFA and passkey support, administrative controls, export options and incident-response process. Protect the vault with a strong, unique primary password and MFA, keep devices updated and lock them whenever they are unattended.
Password controls work best as part of a wider programme covering identity and access management, software updates, incident reporting and staff awareness. The Human Focus guide to choosing a security awareness training platform explains how organisations can connect learning to role-specific risks, reporting and programme ownership.
The Cyber Security Awareness Training course introduces employees to common attacks and practical password, MFA and online-safety habits. Awareness training supports wider organisational controls, but it does not replace secure system configuration, access management or role-specific procedures.