Regardless of the type of business you operate, it’s likely that you’ll have to deal with personal information. Employee details, customer information and even your own personal information must be secure.
The need for business owners to protect personal data is a legal duty under the UK GDPR. This guide covers 10 essential data protection methods that help businesses meet their security responsibilities.
The EU General Data Protection Regulation (GDPR) became applicable in May 2018. Since January 2021, the UK has had its own version, the UK GDPR. It works alongside the Data Protection Act 2018. The Data (Use and Access) Act 2025 amends these laws without replacing them.
The UK GDPR provides individuals with more control over their personal data, how it is used and who has access to it. Personal data is information relating to an identified or identifiable individual. Examples include a person’s:
- Name
- Photo
- Email address
- Banking details
- Social media account details
- Medical information
- IP address
- Location
- Race
- Ethnic background
- Religious beliefs
- Trade union membership
- Biometrics
- Health
- Genetics
- Sexual orientation or sex life
Some of these are special category data, including health information, racial or ethnic origin and religious beliefs. Biometric data is special category data when used to uniquely identify someone. These categories require additional safeguards.
Since 19 June 2026, organisations must also provide a way to raise data protection complaints, acknowledge them within 30 days and respond without undue delay (ICO, 2026a).
The Cyber Security Breaches Survey 2025/2026 found that 43% of UK businesses identified a cyber security breach or attack in the previous 12 months (DSIT, 2026). Separately, the ICO received 17,431 personal data breach reports in 2025/26. This is a count of reports received, rather than distinct incidents (ICO, 2026b).
Complying with the UK GDPR means processing personal data securely using appropriate technical and organisational measures. The Information Commissioner’s Office (ICO) can restrict processing, suspend data transfers or issue administrative fines.
For the most serious infringements, the higher maximum fine is £17.5 million or 4 per cent of total worldwide annual turnover in the preceding financial year, whichever is greater (ICO, Data Protection Fining Guidance).
While the requirements of the UK GDPR can seem daunting at first, the following methods provide practical ways to strengthen data security. Compliance also requires lawful processing, transparency, respect for individual rights and accountability.
A data protection risk assessment identifies risks to personal data and assesses their likelihood and severity for the people affected. Data protection methods should then be put in place to eliminate or control these risks.
Identify what information is held, why it is needed and who handles it, including suppliers. Only collect and retain the personal data needed for the purpose.
A formal data protection impact assessment (DPIA) is required where processing is likely to result in high risk to individuals. A data protection officer (DPO) is mandatory only in specified circumstances, although specialist advice may help with the assessment.
Important business data should be regularly backed up. Backups should be kept in a safe, secure space with restricted access and appropriate encryption.
Tape storage and portable hard drives remain options, alongside managed cloud backups. Keep at least one copy offline or otherwise isolated from live systems so an attack cannot affect every copy, and regularly test that data can be restored (NCSC, Backup Guidance).
Encryption helps protect personal data if it is intercepted, lost or accessed without permission.
The UK GDPR requires security appropriate to the risk, rather than a particular encryption method for every processing stage.
Use secure connections, such as HTTPS/TLS, for data in transit and appropriate encryption for devices, backups and stored information. Protect encryption keys separately and restrict access to them (ICO, Encryption Guidance).
Businesses handling payment card data should also check the relevant PCI DSS requirements. PCI DSS is a separate payment card security standard.
Pseudonymisation is a data protection method recognised by the UK GDPR. This technique involves replacing or removing information that directly identifies a person and keeping the additional identifying information separately.
For instance, a list of names could be replaced by randomly generated numbers. This can reduce risks to people’s identities and sensitive information. Pseudonymised information remains personal data and is still subject to data protection law.
Only trained and authorised employees should be given access to personal data, and personal data should only be accessed when there is a clear business reason for doing so.
Give users only the access needed for their role, review permissions regularly and remove access promptly when staff leave.
Enable multi-factor authentication (MFA), particularly for email, cloud services and administrator accounts. Where supported, use phishing-resistant methods such as passkeys or security keys. Apply zero-trust principles by checking identity, device condition and access permissions rather than assuming that someone on the company network can be trusted (NCSC, MFA Guidance; NCSC, Zero Trust Guidance).
It is helpful to draft a data protection policy that will inform employees of their roles and responsibilities. A related cyber security policy should set out security controls and incident reporting procedures.
The UK GDPR requires personal data to be kept for no longer than necessary for its purposes. Set retention periods that account for relevant legal obligations, then securely erase or anonymise information when it is no longer needed.
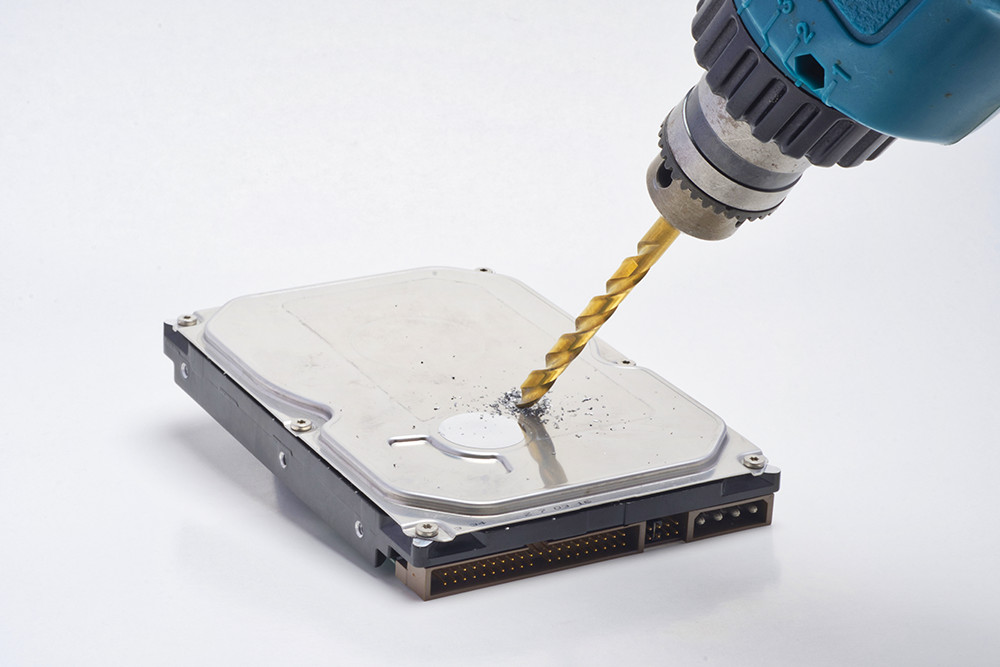
IT infrastructure often needs to be upgraded and replaced. When replacing a computer, securely sanitise its storage before disposal or reuse.
Use a method appropriate to the storage media, such as secure erasure or physical destruction. Degaussing is suitable only for appropriate magnetic media and does not erase SSDs or other flash storage.
Paper documents should be disposed of securely, for example through confidential shredding. A suitable disposal provider can be used; there is no blanket requirement for on-site shredding (ICO, Disposal Guidance; NIST, 2025).
Data breaches caused by viruses or malware remain a risk. Protecting IT infrastructure requires appropriately configured firewalls and up-to-date anti-virus or anti-malware protection.
Keep operating systems, applications and firmware updated, and replace unsupported software or devices. Regular scans help identify threats, but cannot guarantee network security (NCSC, Device Security Guidance).
File sharing between devices may be necessary for your business. If so, ensure that wireless networks use secure encryption and strong, unique passwords.
Change default router administrator credentials, keep router firmware updated and separate guest access from business systems.
Disable unnecessary public sharing and use approved secure connections for remote access.
If employees conduct business activities via their mobile phones, business and personal data should be kept separate.
This can be done through a mobile device management system that controls access to business information and, where supported, provides a separate work container.
Alternatively, issue staff with devices that are used only for business purposes. Enable device encryption, screen locks and updates. Where appropriate, enable remote wiping, limiting it to work data on personal devices. Any location tracking should be necessary, proportionate and explained to staff.
The UK GDPR generally applies to personal data processing connected with organisations established in the UK. EU GDPR may also apply, for example where a UK business offers goods or services to people in the EU or monitors their behaviour there. Applicability is not determined simply by citizenship.
Employees should understand their responsibilities and individuals’ rights under applicable data protection law. Training should cover secure sharing, checking recipients, recognising phishing and suspicious requests, and reporting incidents promptly. Staff should only enter personal data into AI tools through authorised processes that protect the information.
Keep a record of all personal data breaches and assess the risk to individuals. Where notification is required, report the breach to the ICO without undue delay and, where feasible, within 72 hours of becoming aware. Inform affected individuals without undue delay where the breach is likely to pose a high risk to their rights and freedoms (ICO, Personal Data Breach Guidance).
If a business breaches data protection law, the consequences can be severe. Leaking sensitive data can harm individuals and damage the business’s reputation.
Human Focus GDPR Awareness Training introduces GDPR principles, individual rights and responsibilities for handling personal data. The CPD-certified course can be taken online. Learners who successfully complete the assessment receive a certificate of completion.
Online awareness training cannot replace organisational policies, technical security controls or specialist data protection advice.