Business email compromise (BEC) is a form of fraud that uses seemingly genuine workplace emails to steal money or sensitive information. Criminals may pose as a senior manager or supplier and ask an employee to make a payment, change bank details or share confidential records.
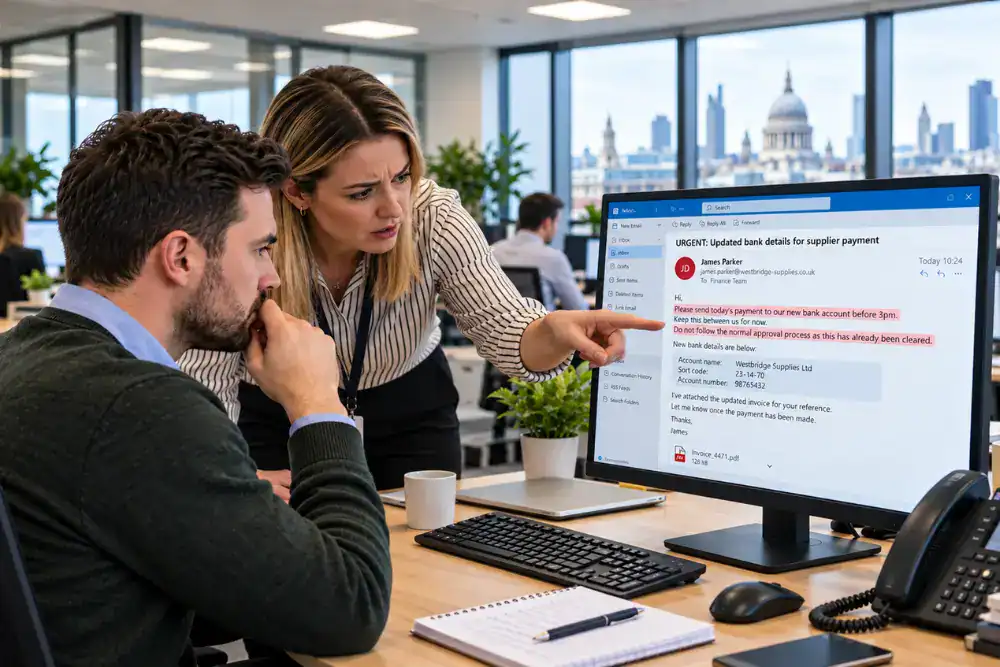
The email may look routine and appear to come from your finance director. It may ask you to pay a supplier using new bank details today and to “keep this between us for now”. If the request is fraudulent, the payment could go to an account controlled by criminals.
UK Finance’s 2025 figures show that invoice and mandate scams cost victims about £17,900 per case on average, while chief executive officer (CEO) fraud cost about £28,400. Both were substantially higher than the average of around £2,300 across all Authorised Push Payment (APP) fraud.
Security tools that scan for malicious links or attachments may miss a BEC email containing only a believable request. The risk comes from acting on that request, so employees still need to verify unusual instructions through a trusted channel. This guide explains what BEC is, how attacks unfold, the warning signs and the simple checks that can stop them.
Business email compromise is a type of email fraud in which criminals pose as someone you trust, such as a manager, colleague or supplier. Their goal is to trick you into sending money or sensitive information to them, as the City of London Police’s Report Fraud service explains.
You may also hear it called Payment Diversion Fraud (PDF) or Mandate Fraud. The Report Fraud service uses all three names. UK Finance, which publishes the banking industry’s fraud figures, reports the losses as “invoice and mandate scams” and “CEO fraud”.
Criminals get into position in two main ways:
- They register a lookalike email address or domain, or change the display name, so a message seems to come from someone you know.
- Account takeover. They break into a real mailbox, often with a stolen password, and send requests from a genuine address, sometimes inside an existing email thread. A hacked account can also let criminals reset passwords to get into other accounts.
BEC is often described as a targeted form of phishing. The difference is that:
- Ordinary phishing targets a large number of people at once with generic messages that often contain a malicious link or attachment.
- Business email compromise targets specific people who can approve payments or release data. It is more researched and built around a single convincing request.
For more on related tactics such as spear phishing, whaling and email spoofing, see Recognising Common Cyber Security Threats.
A BEC attack typically moves through five main stages:
- Research. Criminals study the organisation, its leaders and its suppliers. The Take Five to Stop Fraud campaign, run by UK Finance, warns that criminals may spend several months on research, such as collecting employee and supplier information from online sources. AI can help criminals speed up this research.
- Disguise or access. They set up a lookalike email address or take over a real mailbox belonging to a colleague, senior leader or supplier.
- Watch and wait. Once inside a compromised mailbox, they can read real conversations to learn who approves payments, when invoices fall due and how people write.
- The request. A message asks for an urgent payment, new bank details for a supplier or sensitive records.
- Cash-out. The money lands in an account the criminal controls. The Report Fraud service advises telling your bank as soon as possible to help prevent further losses.
Knowing these three types makes an unusual request easier to recognise.
CEO fraud is a scam in which a criminal impersonates a chief executive or senior manager to trick an employee into making a payment. The request is usually urgent.
The trick is no longer limited to email. The government’s Stop! Think Fraud campaign warns that criminals sometimes use deepfake audio or video of senior executives.
In 2024, engineering firm Arup confirmed that an employee in Hong Kong had transferred HK$200 million, about £20 million, to criminals. The employee had joined a video call in which deepfakes generated by artificial intelligence (AI) impersonated senior officers.
Invoice fraud targets payments you already expect to make. A criminal poses as a genuine supplier and claims its bank details have changed, so the next invoice is paid into the criminal’s account instead.
It also works in reverse. If criminals take over your mailbox, they can send your customers fake invoices or new bank details in your name.
Not every BEC attack asks for money straight away. Some request sensitive information, such as staff records or financial documents, which can fuel further fraud.
Others target payroll. Stop! Think Fraud warns of salary diversion fraud, in which scammers pose as employees and ask human resources (HR) or payroll teams to change bank details.
Our guide to types of workplace fraud covers insider schemes such as payroll and supplier fraud.
Businesses bear the brunt of invoice fraud. According to UK Finance’s Annual Fraud Report 2026, business accounts suffered more than two-thirds of invoice and mandate scam losses in 2025. UK Finance explains that firms make genuine high-value payments regularly, which makes a fraudulent one harder to spot.
Invoice scam cases against businesses fell by 7% in 2025, yet the number of fraudulent payments rose by 11%. Each successful scam therefore involved more payments on average. CEO fraud cases against businesses fell by 29%, but CEO fraud still has the highest average loss of the eight scam types UK Finance tracks.
There is good news too. Losses to invoice and mandate scams and CEO fraud fell in 2025. UK Finance puts this down to continued industry investment in fraud prevention and customer education and awareness.
Even so, average losses per case for these two scam types were roughly eight to 12 times the APP fraud average, and less than half the money lost was returned. Across all types of APP fraud, cases against non-personal (business) accounts rose by 13% to 7,504, while losses fell by 11% to £75.6 million.
AI is raising the stakes. The NCSC warns that generative AI can produce convincing messages without the translation, spelling and grammatical mistakes that often reveal phishing. Its 2025 assessment judges that AI will almost certainly make cyber threats more frequent and more intense between now and 2027.
For small and medium-sized enterprises (SMEs), a single diverted five-figure payment can do lasting damage. Our article on growing cyber threats to small businesses explains why no organisation is too small to be targeted. Larger organisations have more suppliers, more approvers and more inboxes to protect, which gives criminals more ways in.
Treat any email that involves money or data with extra care, and watch for these red flags:
- Urgency or secrecy. Pressure to act now or keep the request quiet is a classic tactic, according to Report Fraud.
- New or changed bank details. Any request to pay a different account, especially when it arrives by email alone.
- Pressure to skip the process. A request to bypass approvals, purchase orders or the usual sign-off.
- A sender that is almost right. A lookalike domain, a personal webmail address or a display name that does not match the address behind it. Check the reply-to address too.
- An unexpected request from a familiar name. Take Five warns that unexpected requests for urgent payment can appear to come from someone in your own business.
- A change of tone or channel. A colleague who writes differently from usual, or who avoids a quick phone call to confirm.
- Requests for sensitive data. Staff records, payroll files, passwords or financial documents.
Perfect spelling is no longer reassuring. AI can remove the errors that once gave scams away, so judge the request itself rather than the writing.
Follow these steps whenever an email involves money, bank details or sensitive data.
- Pause before you act. The Take Five to Stop Fraud campaign urges you to stop and think. At work, that means you can hold any unusual request until you have checked it.
- Verify through a different channel. Call the person on a number you already have; never use a channel given in the same email. For bank detail changes, Stop! Think Fraud advises confirming both the old and new account details using a known phone number.
- Follow the payment process every time. Do not skip an approval because a request seems senior or urgent. A sender who asks you to bypass a check is a red flag in itself.
- Check the payee name. When you set up a new payee, your bank’s Confirmation of Payee service checks the name on the account. Treat a mismatch as a reason to stop and verify.
- Report it straight away. If you have reason to suspect fraud, tell your information technology (IT) or security team and follow your organisation’s reporting process even if you are unsure. You can also forward suspicious emails to the NCSC at report@phishing.gov.uk.
- If money has gone, act fast. Contact your bank using its official website or phone number, as the NCSC advises. Then report it to Report Fraud online or on 0300 123 2040, or to Police Scotland on 101 if you are in Scotland.
- Protect your own account. Use a strong, unique password with multi-factor authentication (MFA), or a passkey where available, as the NCSC recommends. Our guide to password security explains how to create strong passwords and use MFA.
- Think before you share. Criminals use public details such as staff names, job titles and supplier details to make requests convincing. Keep what you post about work to a minimum.
Employee vigilance works best when the organisation backs it with clear rules and the right technology. These controls suit SMEs and enterprises alike:
- A written payment verification process. Require a call-back to a known number for every new payee or bank detail change, plus dual approval above a set value. Stop! Think Fraud also recommends sign-off processes and delay periods for changes to bank or payroll details. For large transfers, Report Fraud suggests sending a small test payment first.
- A clear rule on executive requests. If your chief executive or finance director will never contact staff to ask for urgent payments, make sure everyone knows it, as Stop! Think Fraud recommends.
- Email authentication. Set up Domain-based Message Authentication, Reporting and Conformance (DMARC), Sender Policy Framework (SPF) and DomainKeys Identified Mail (DKIM). The NCSC’s email security guidance explains how they make your domain harder to spoof.
- MFA on email and finance systems. With multi-factor authentication, the NCSC notes, an attacker cannot get into an account with a stolen password alone. Yet only 47% of businesses use two-factor authentication, according to the Cyber Security Breaches Survey.
- Less information for attackers. Review what your website and social media reveal about senior staff, suppliers and payment processes.
- Regular, practical training. Only 19% of businesses ran staff training or awareness activities in the last 12 months, the same survey found.
- A no-blame reporting culture. The NCSC advises organisations not to reprimand staff who struggle to recognise phishing emails. People who feel safe owning up to a mistake report it sooner.
- An incident response plan. Only 25% of businesses have a formal plan, the survey found. Your response plan should cover contacting the bank, securing the mailbox and reporting the crime. Our guide to writing a cyber security policy covers reporting procedures.
- A route for data breaches. If a compromised mailbox exposes personal data, assess the risk quickly. Where a risk to people is likely, the Information Commissioner’s Office (ICO) must be told as soon as possible and, where feasible, within 72 hours. Our guide to data breach reporting explains the process.
SMEs should separate duties where possible, so the person who receives a bank detail change is not the only one who approves it. In larger organisations, restrict who can edit supplier bank details in finance systems and review every change.
Do not rely on getting the money back. Mandatory reimbursement rules cover only individuals, micro-enterprises and smaller charities.