In short: Vishing is a type of phishing carried out by voice. A fraudster calls while pretending to be a trusted person or organisation and tries to persuade you to disclose sensitive information, transfer money, provide account access or take another action (NCSC, 2022a). Unlike email phishing or smishing, vishing relies on a phone call or other voice interaction. If a caller asks for money, credentials, sensitive information or access, verify the request independently through a trusted contact method before acting.
What Is Vishing? How Voice Phishing Scams Work
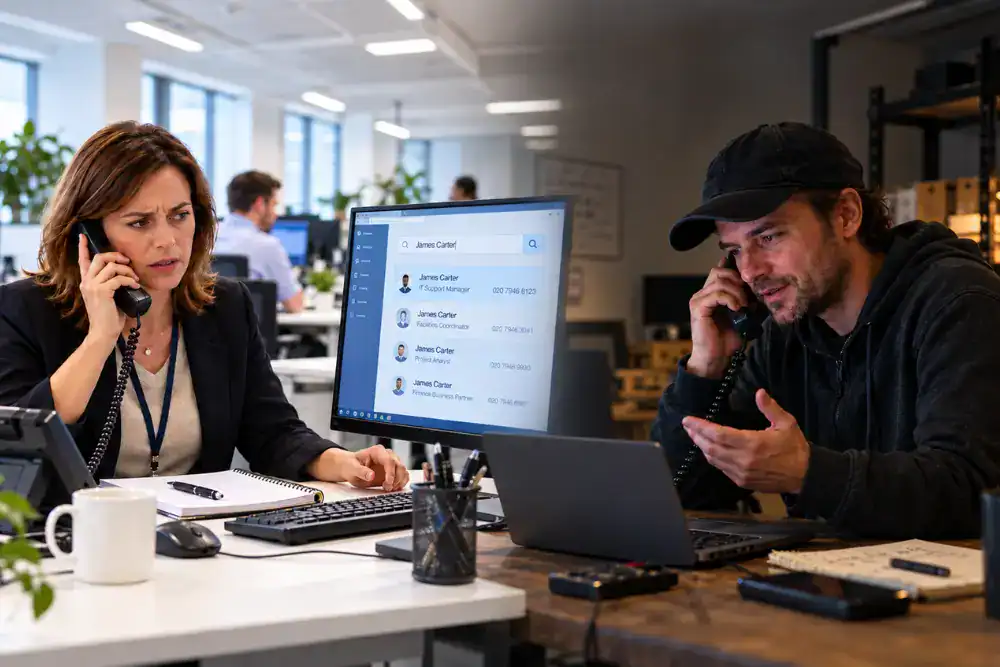
Employees regularly receive genuine calls from banks, suppliers, colleagues, IT support teams and public bodies. Some are unexpected and some require prompt action. That gives fraudsters an opportunity to make a false request look like routine work.
A caller may know someone’s name, job role, supplier relationship or recent activity. They may also make a familiar telephone number appear on the recipient’s screen. UK telephone networks cannot reliably confirm to the recipient who originated a call, so the displayed number is not proof of identity (NCSC, 2026a).
For employees, the key question is therefore not whether the caller sounds convincing. It is whether the request involves an action that should be independently verified before money, information or access is provided.
How Does Vishing Work?
Vishing combines a credible identity or situation with a request that has consequences. The details vary, but the pattern usually follows five stages.
- The caller chooses a credible identity. They may claim to represent a bank, supplier, public body, senior colleague or internal support team.
- Public information, stolen data or details exposed elsewhere can give the caller enough knowledge to make the call sound relevant and informed.
- A spoofed caller ID can make the call appear to come from a known number, while familiar terminology or references to a real process can strengthen its appearance of legitimacy.
- Urgency, authority, concern or secrecy can reduce the opportunity to check by making it feel difficult or unsafe to pause.
- The call then moves towards a consequential request involving a password, one-time passcode, payment, new payee, remote access, software installation or confidential information.
Report Fraud confirms that fraudsters may use number spoofing, personal details and urgent stories to make phone fraud more convincing (Report Fraud, n.d.). Artificial intelligence voice cloning is another possible impersonation method. It does not change the safe response. Whether the voice is human, automated or synthetically generated, the request still needs to follow the organisation’s verification and approval process.
Vishing Examples in the Workplace
The story changes according to the employee’s role, but the risky moment is consistent. An unexpected caller wants an action completed before the normal check takes place.
A Bank or Fraud Team
The caller refers to an apparently genuine transaction or account detail and says immediate action is needed. They ask for a one-time passcode, security information or a transfer to a supposedly safe account.
End the call. Contact the bank using the number on the back of the card, a number held in the organisation’s records or the 159 service. Do not use a number supplied by the caller.
Internal IT or Technical Support
The caller knows the employee’s name, role or internal terminology. They say an account or device is at risk and ask for a password, multi-factor authentication approval, software installation or remote access.
End the call and contact IT through the approved helpdesk or internal directory. A genuine technical problem can still be handled through the known route.
A Supplier or Service Provider
The caller refers to a real supplier relationship, invoice or delivery. They request changed bank details, an urgent payment or sensitive account information.
Verify the request using the supplier record already held by the organisation and follow the approved process for account changes and payments. Familiar commercial details do not remove the need for that check.
A Senior Colleague
The caller claims there is a confidential or urgent business need. They ask the employee to bypass an approval, release information or arrange a payment before speaking to anyone else.
Use the internal directory or another established channel to contact the colleague. Seniority and urgency should not displace the normal authorisation process.
Official UK guidance identifies requests for payments, personal or financial information, passcodes and remote access as common features of phone fraud (Stop! Think Fraud, n.d.a).
How to Spot Vishing
An unexpected call warrants a check but does not, by itself, prove fraud. The strongest warning signs concern what the caller wants you to do and whether they want to bypass a trusted process.
Stop and verify when a caller:
- asks for a password, PIN, one-time passcode or multi-factor authentication approval
- asks for a payment, transfer, new payee or change to bank details
- asks you to install software or allow remote access to a device
- requests personal, commercial or confidential information that would not normally be provided by phone
- wants to bypass a callback, second approval, helpdesk route or other established control
- creates urgency, panic, authority or secrecy around the request
- discourages you from checking with a colleague or contacting the organisation independently
- treats a familiar number, known detail or professional manner as proof of identity
- introduces an unexpected change to a familiar process
Ofcom advises people to be cautious about unexpected contact, requests for personal or financial details, secrecy and urgency. It also advises calling the organisation back using the number on its official website rather than one provided by the caller (Ofcom, 2026).
Accents, pauses, background noise and voice quality are not dependable tests. A genuine caller may sound unusual and a fraudulent caller may sound entirely professional. Employees should recognise requests that require verification without trying to prove that a voice is fake.
Anatomy of a Vishing Call
Consider an apparent internal IT caller who says unusual activity has been detected and asks an employee to approve a multi-factor authentication prompt so the account can be secured.
- Apparently credible caller: The person uses internal terminology and knows the employee’s name.
- Unexpected context: The employee did not raise a support request.
- Pressure: The caller says the account will be locked unless the employee acts immediately.
- Sensitive action: The employee is asked to approve an authentication prompt or provide a code.
- Process bypass: The caller says not to contact the helpdesk because the matter is confidential.
- Safe response: The employee ends the call, contacts IT through the approved directory and reports the attempt.
The unexpected authentication request and the attempt to bypass the helpdesk give the employee sufficient grounds to stop and check.
What Should You Do If You Suspect Vishing?
Employees need a response that still works under pressure.
- Stop the interaction. End the call. Do not continue answering questions, press requested buttons, install software or act on the request.
- Verify through a trusted route. Use the internal directory, approved helpdesk, supplier record, official website, number on a bank card or another contact route held independently of the call.
- Do not use contact details supplied by the caller. A callback number, link or website given during the interaction may lead back to the fraudster.
- Report or escalate the concern. Follow the organisation’s procedure so the appropriate IT, finance, security, data protection or management function can assess it.
Ending a call is a legitimate security action, even when the caller claims urgency or authority. A genuine organisation can continue the conversation once contact has been re-established through an independent route.
Report Fraud advises people to report a suspicious call to their mobile provider by texting Call followed by the caller’s number to 7726 (Report Fraud, n.d.). If money has been lost or an account has been hacked, report the incident to Report Fraud in England, Wales or Northern Ireland. In Scotland, contact Police Scotland on 101 (Report Fraud, 2025). Workplace reporting should still happen first or at the same time so the organisation can assess its own exposure.
What If You Have Already Shared Information or Taken Action?
Report the incident immediately through a trusted route. Quick disclosure gives the organisation, bank or service provider the best opportunity to protect accounts, contain access and respond to a payment. It is not too late to act and the employee should not investigate the incident alone.
A Work Password or Account Access Was Provided
Contact IT or security immediately. Follow the organisation’s process for securing the account and changing affected passwords. If the same password was used elsewhere, those accounts may also need to be secured. The NCSC advises contacting the IT department when a suspicious interaction affects a work laptop or phone (NCSC, 2022b).
Personal or Banking Information Was Shared
Contact the bank or relevant provider immediately through a trusted number, even if no loss is visible. Stop! Think Fraud advises notifying the bank as soon as sensitive banking information may have been shared so it can protect the account (Stop! Think Fraud, n.d.b).
A Payment or Transfer Was Made
Contact the bank or payment provider immediately, then inform the organisation’s finance or incident lead. Fast action may improve the chance of stopping or recovering a payment, although recovery cannot be guaranteed (Stop! Think Fraud, n.d.c). Use the appropriate police reporting route as well.
Remote Access Was Granted or Software Was Installed
End contact with the caller and notify IT or security through a trusted channel. Leave containment and remediation to the people responsible for the organisation’s systems.
Confidential Work Data Was Disclosed
Use the organisation’s incident, privacy or data protection route immediately. The responsible team can assess what was disclosed, who may be affected and what further action is required.
A reporting process works only if people can use it after a mistake as well as before one. Blame and delay make containment harder. The NCSC advises organisations to avoid a punishment-led culture and support people who report after they have acted (NCSC, 2026b).
What Should Employers Reinforce Beyond Training?
Employees can follow a secure process only when the organisation makes that process clear and workable. Employers should:
- publish trusted contact routes for IT, finance, HR, suppliers and incident reporting
- define which requests require an independent callback or second approval
- prevent urgency or seniority from overriding payment, account-change and access controls
- keep internal directories and supplier records current
- make reporting quick and non-punitive, including after an employee has acted
- use appropriate authentication, access restrictions, payment controls and incident procedures
- make legitimate calls consistent and explain what employees will never be asked to disclose or approve by phone
The NCSC recommends making important requests more resistant to phishing through independent verification and keeping reporting clear, simple and quick (NCSC, 2026b). Its telephone guidance also advises organisations to use consistent contact details and give people a route to initiate contact themselves (NCSC, 2026a).
These controls sit within the wider task of managing digital fraud in the workplace. The aim is to give already busy employees a clear, supported way to act safely when a suspicious request arrives.
What Vishing Awareness Training Should Enable Employees to Do
Useful awareness training should give employees a shared response and make clear that no one can correctly classify every call. They should understand how caller impersonation works and recognise requests involving money, credentials, data or access that require an independent check.
Training should also make clear that caller ID, known details and a convincing voice are not proof of identity. Employees need to know how to resist pressure, use the organisation’s trusted contact routes and report quickly after a concern or accidental action.
Training is one part of a layered defence. The NCSC warns against placing too much emphasis on users spotting every phishing attempt and recommends a combination of technical, process and people-based controls (NCSC, 2026b). Awareness cannot replace payment approvals, access controls, call screening, secure authentication or incident response.
Human Focus Cyber Security Awareness Training covers recognition and response across phishing, vishing and social engineering. Its dedicated vishing content includes fraudulent calls, robocalls and deepfake voices, alongside employees’ responsibilities for following organisational policy and reporting concerns.
Give employees a consistent way to recognise, verify and report suspicious requests before money, information or access is provided.