In short: Cyber security awareness training teaches employees how to recognise common online threats, protect business information and respond appropriately to suspicious activity. For UK employers, training is an important organisational security measure that supports the protection of systems and personal data. An effective programme combines relevant learning, clear workplace procedures and regular reinforcement rather than relying solely on course completion.
Cyber Security Awareness Training: A Guide for UK Employers
Cyber security awareness training helps UK employers equip their staff with the knowledge and practical skills needed to recognise online threats and follow safer working practices. This guide explains what training should cover, who needs it and how organisations can make it effective.
Employees regularly handle emails, passwords, business documents and digital systems. Their decisions can influence the organisation’s exposure to cyber threats, even when technical security controls are in place.
Employers therefore need an approach that reflects the risks employees encounter during their work. Understanding the content, delivery and evaluation of cyber security training can help organisations develop a proportionate and practical awareness programme.
What Is Cyber Security Awareness Training?
Cyber security awareness training is structured learning that helps employees understand common cyber threats and the actions they can take to protect workplace information, devices and systems.
The training typically covers phishing, password security, suspicious websites, malicious software, safe internet use and the reporting of potential security incidents.
Rather than teaching employees to become technical security specialists, awareness training focuses on recognising risks and making appropriate decisions during routine work.
For example, a finance employee may need to recognise a fraudulent request to change supplier bank details. An HR administrator may need to identify attempts to obtain confidential employee information. A site supervisor using a shared device may need to understand secure access and account protection.
The National Cyber Security Centre (NCSC) recommends that organisations develop staff awareness and training arrangements suited to the way their business operates (NCSC, n.d.).
Effective awareness training also makes clear what employees should do when something appears suspicious and how they can obtain support.
Why Is Cyber Security Awareness Training Important for UK Businesses?
Cyber security awareness training is important because employees may encounter fraudulent communications, unsafe links and attempts to gain unauthorised access during normal business activities.
The UK Government’s Cyber Security Breaches Survey 2025/2026 found that 43% of businesses identified a cyber security breach or attack in the preceding 12 months. Phishing was the most commonly identified type, reported by 38% of all businesses surveyed (DSIT, 2026).
These figures describe breaches or attacks identified by surveyed organisations, rather than the proportion of successful attacks or the number directly caused by employee mistakes.
Recognising Fraudulent Communications
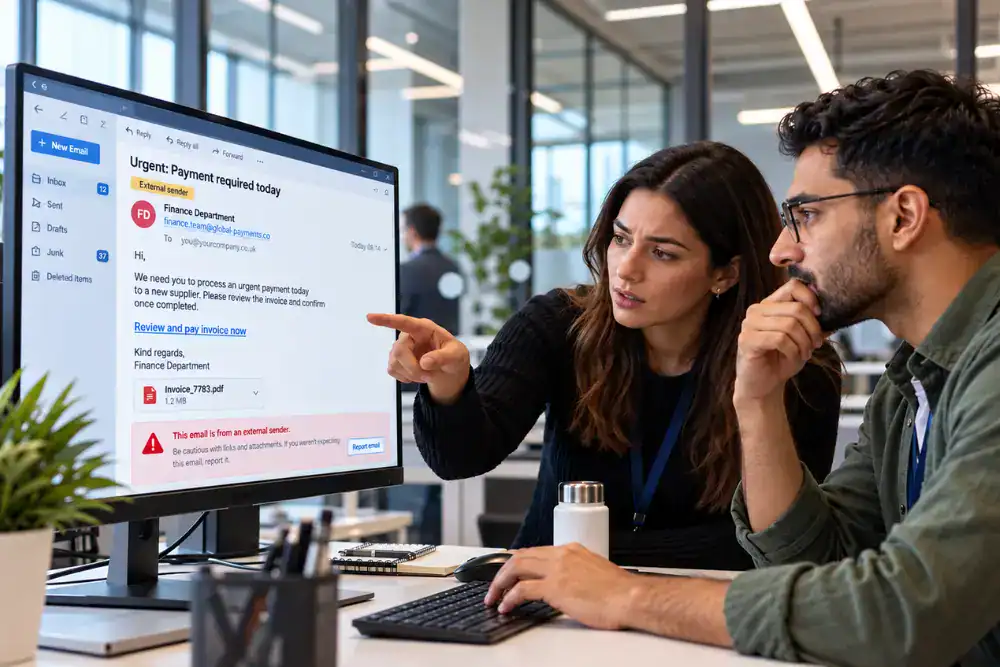
Phishing messages may impersonate colleagues, suppliers, banks or other trusted organisations. Some attempts aim to obtain passwords; others encourage employees to authorise payments or disclose confidential information. Training helps staff recognise suspicious requests and understand independent verification.
Protecting Sensitive Business Information
Employees may handle financial records, customer information, personnel files and commercially sensitive documents. Awareness training can reinforce rules for accessing, storing and sharing information securely.
Supporting Incident Reporting
Early reporting gives IT and security teams an opportunity to investigate suspicious activity and take appropriate action. The NCSC recommends clear reporting processes and a supportive environment where staff can raise concerns, including when they may already have clicked a suspicious link (NCSC, 2018).
Is Cyber Security Awareness Training Mandatory in the UK?
There is no general UK law requiring every employer to purchase a particular cyber security awareness course or deliver training at one fixed interval.
However, organisations processing personal data must meet applicable security obligations under the UK General Data Protection Regulation (UK GDPR) and the Data Protection Act 2018.
Article 32 of the UK GDPR requires controllers and processors to implement appropriate technical and organisational measures to ensure a level of security appropriate to the risk. Appropriate measures depend on factors including the nature of processing, the risks involved and the state of the art.
The Information Commissioner’s Office (ICO) identifies staff awareness, initial training and refresher training as important organisational measures for protecting personal information (ICO, n.d.-a).
Training alone does not establish UK GDPR compliance. Organisations also need suitable technical safeguards, access controls, policies and incident management arrangements appropriate to their circumstances.
Some organisations face additional cyber security requirements arising from their sector, contractual commitments or services. Those obligations should be assessed separately.
What Should Cyber Security Awareness Training Cover?
Cyber security awareness training should cover the threats employees are likely to encounter and the safe working practices relevant to their roles.
Phishing and Social Engineering
Employees should understand deceptive emails, fraudulent text messages, suspicious links and requests that appear to come from trusted contacts. Social engineering means attempts to manipulate people into taking actions that benefit an attacker. Staff need to know how to verify unusual instructions, particularly requests involving money, passwords or confidential information.
Password Security and Multi-Factor Authentication
Training should explain why weak or reused passwords can expose accounts to unauthorised access, how to use approved password managers and why login details should not be shared. Multi-factor authentication (MFA) adds a further identity check. Unexpected authentication requests should be treated with caution.
Safe Internet and Device Use
Employees should understand suspicious downloads, malicious websites, unapproved applications and unsecured devices.
- Keeping devices and software updated
- Using approved applications and services
- Following company rules for removable storage
- Locking devices when unattended
- Using secure connections when working remotely
- Reporting lost or stolen workplace equipment
Business Email Compromise
Business email compromise (BEC) involves fraudulent communications intended to manipulate business decisions, commonly involving payments or sensitive information. Training should explain how attackers impersonate managers and suppliers and why bank-detail changes must be verified through established procedures.
Voice Phishing and AI-Enabled Fraud
Voice phishing, or vishing, involves fraudulent telephone or voice communications. Some attacks may use AI-generated voices to impersonate individuals. A familiar-sounding voice is not sufficient proof of identity when a caller requests sensitive information or financial action.
Data Protection and Incident Reporting
Employees should know which information they are authorised to access, how it should be handled and whom to contact after a suspicious email, accidental disclosure or lost device. The ICO recommends appropriate employee training on protecting personal information and recognising deception (ICO, n.d.-a).
Who Needs Cyber Security Awareness Training?
Cyber security awareness training is relevant to employees who use workplace digital systems, access business information or communicate electronically. The level and content should reflect individual responsibilities and exposure.
Office and Administrative Employees
Administrative staff handle correspondence, shared files and internal systems. They need guidance on suspicious communications, passwords, attachments and information handling.
Finance and Payroll Teams
Finance employees may be targeted through invoice fraud, supplier impersonation and fraudulent payment instructions. Their training should emphasise payment verification and approval procedures.
HR and Recruitment Employees
HR teams work with employee records and recruitment documents. Their training should address confidentiality, secure document sharing, access permissions and fraudulent information requests.
Managers and Senior Leaders
Managers may have privileged access or approve payments. They should understand how impersonation exploits authority and how their own approval practices can support security.
Remote Workers and Contractors
Remote employees and contractors may access systems from different locations. Training should address approved equipment, account protection and reporting, based on the access granted.
How Often Should Employees Complete Cyber Security Awareness Training?
Cyber security awareness training should be provided at intervals appropriate to employees’ responsibilities, organisational risks and changes in working practices or threats.
There is no single general statutory renewal period applying to all UK workplace cyber security awareness courses.
The ICO’s training and awareness guidance recommends suitable induction and refresher training, supported by updates when risks or requirements change (ICO, n.d.-b).
An employer might provide initial training when employees receive access to systems, annual refreshers and shorter updates for emerging scams. An annual schedule should not be treated as a universal legal requirement or guarantee of effectiveness.
Additional training may be appropriate after role changes, increased access privileges, new categories of information or unfamiliar security risks.
How Can Employers Deliver Effective Cyber Security Awareness Training?
Employers can deliver effective training by identifying risks, selecting suitable learning, reinforcing safe practices and checking whether staff understand the required actions.
1. Identify Workplace Cyber Risks
Review how staff use business systems and information. Consider who handles payments, personal information, supplier communications or privileged accounts.
2. Define Clear Learning Outcomes
Specify what staff should recognise and do. A finance employee may need to verify bank-detail changes; general office staff may need to identify and report suspicious emails.
3. Choose an Appropriate Delivery Method
Training can be online, instructor-led or blended. Delivery should reflect locations, shifts, accessibility needs and the tasks employees perform.
4. Connect Training to Workplace Procedures
Explain actual procedures for incident reporting, verifying payments and protecting information. Staff should leave knowing whom to contact.
5. Reinforce Learning Over Time
Use short reminders, incident examples and team discussions. Managers should encourage timely reports without unnecessary blame.
6. Review Training Effectiveness
Attendance and test results show participation and knowledge at assessment, not necessarily real-world behaviour. Employers can also review reporting processes, feedback and relevant incidents.
How Can Employers Choose the Right Cyber Security Awareness Training?
Employers should choose training that reflects their workforce, workplace risks and learning requirements. The content should use clear language and explain practical actions.
- Relevant coverage of cyber threats
- Practical workplace scenarios
- Accessible formats
- Useful assessment options
- Training records where appropriate
- Opportunities to update or reinforce learning
Organisations with multiple teams may need a system for assigning courses, monitoring completion and reviewing records.
For more detail, see the Human Focus guide, Security Awareness Training Platform: How to Choose the Right Solution for Your Organisation. Read the training platform guide.
A training platform can support programme administration, but employers remain responsible for relevant learning, workplace procedures and reinforcement.
How Can Employers Measure Cyber Security Awareness Training Effectiveness?
Employers can evaluate effectiveness by examining learning outcomes and whether staff understand and follow secure procedures.
Training completion: Records show participation and refresher dates.
Knowledge assessment: Tests indicate understanding at the time of assessment.
Incident reporting: Review whether staff know how to raise concerns promptly; higher reporting numbers may indicate better awareness rather than worsening security.
Workplace procedures: Check whether staff follow payment verification, information handling and incident reporting processes.
Employee feedback: Invite staff to identify unclear instructions and obstacles to safe working.
The ICO’s accountability guidance encourages organisations to review training effectiveness and employees’ understanding of information-handling responsibilities (ICO, n.d.-c). No single measure proves that training prevented an incident.
How Does Cyber Security Awareness Training Support a Safer Workplace?
Cyber security awareness training helps employees identify suspicious activity, handle information appropriately and follow established security procedures.
- Training should explain practical actions as well as threats.
- Learning should be supported by secure systems, clear procedures and management.
- Completion records are useful, but understanding and application also matter.
The aim is not to make every employee a cyber security expert, but to make secure verification, reporting and appropriate support part of routine work.
Develop Employee Cyber Security Awareness with Human Focus
Employers seeking to strengthen workplace cyber security awareness need training that helps employees recognise threats and apply safer digital working practices.
Human Focus Cyber Security Awareness Training is a CPD-certified online course designed to introduce employees to common cyber threats and protective behaviours. View the Human Focus course.
The course covers phishing, voice phishing, social engineering, password security, multi-factor authentication and safe digital working. It includes an online multiple-choice assessment and a digital certificate following successful completion.
Explore Human Focus Cyber Security Awareness Training to support your employee awareness programme and reinforce practical cyber security habits.