Most organisations that have experienced a phishing attack can tell you what happened. Fewer can explain whether their training helped staff respond.
Security awareness training is a line item in many IT and compliance budgets. Platforms are licensed, modules are assigned, completion rates are tracked, and boards are told that staff have been trained. Yet a credential can still be stolen via a phishing email that deployed modules claimed to cover. A post-incident review may reveal staff who passed the training, clicked the link, and had no memory of the course at all.
This is not only a technology problem. It is also a procurement and programme design problem. Organisations that get security awareness training right treat platform selection as a behaviour-change question — not a compliance checkbox. A completion dashboard alone cannot show whether staff will respond appropriately to an attack.
This is where security awareness programmes drift. Not into non-compliance on paper, but into the gap between recorded completion and actual human behaviour under pressure.
This article sets out what separates a security awareness training platform that changes how people respond to threats from one that satisfies an audit requirement and nothing else. It covers what your organisation should demand from any platform before committing to a contract.
Library size. Price per seat. SSO integration. These are the questions that dominate most procurement conversations around security awareness training — and they’re all worth asking. The problem is what doesn’t get asked alongside them.
Cyber threats are not uniform. In the UK Government’s Cyber Security Breaches Survey 2025/2026, phishing was by far the most common type of breach or attack, identified by 88 per cent of businesses that identified any breach or attack in that period (DSIT, 2026).
Well-crafted phishing attempts are designed to exploit the conditions under which people actually work — urgency, authority, familiarity and distraction.
A module that explains what phishing looks like in a low-pressure learning environment does not prepare staff for a spoofed invoice request that arrives on a Friday afternoon from an address that differs by one character from their chief financial officer’s. The gap between knowing the concept and responding correctly under operational conditions is where breaches happen.
The mechanism is familiar. Staff complete a security awareness module during induction. The module describes common attack types with illustrative examples. Staff pass an end-of-module assessment. The record is filed. Six months later, the same staff face a targeted spear-phishing attempt tailored to their role, their organisation and their recent activity. The training gave them information. It did not test their judgment.
43 per cent of businesses and 28 per cent of charities reported identifying some form of cyber security breach or attack in the previous 12 months, rising to 69 per cent of large businesses and 65 per cent of medium businesses (DSIT, 2026).
Organisations that treat awareness module completion as their primary human-layer control may overestimate the protection it provides. That gap matters not only operationally, but legally too.
Most security awareness training providers will confidently assure you that their platform aligns with current UK legislation — and that’s exactly the kind of claim that deserves a closer look.
Under the UK GDPR and the Data Protection Act 2018, as amended by the Data (Use and Access) Act 2025, organisations must implement appropriate technical and organisational measures to ensure a level of security appropriate to the risk (ICO, n.d.-a). Staff training is recognised by the Information Commissioner’s Office (ICO) as an organisational measure (ICO, n.d.-b).
The ICO’s guidance on security under the UK GDPR sets out what ‘appropriate’ means in practice. If a personal data breach occurs and the ICO investigates, the question will not be only whether training was completed. It will also be whether the measures in place were appropriate to the nature and scale of the risk your organisation faces (ICO, n.d.-a).
For operators of essential services and certain digital service providers within their scope, the Network and Information Systems (NIS) Regulations 2018 impose additional duties. These include taking appropriate and proportionate technical and organisational measures to manage security risks, which can extend to staff awareness and procedures (UK Government, 2026). A bill to amend and expand these rules is before Parliament, but has not yet become law (UK Parliament, 2026).
Regulatory compliance is a minimum bar. In August 2026, the ICO issued enforcement action against the Metropolitan Police Service after finding shortcomings in data protection training completion, monitoring and governance (ICO, 2026).
Adequacy depends on the organisation’s risks. A generic module catalogue may not address a workforce with materially different risk profiles. The government-endorsed Cyber Essentials standard provides assurance against a recognised baseline of five technical controls; it does not assess the quality of staff awareness training (NCSC, n.d.-a).
A platform can satisfy every standard procurement question and still leave an organisation exposed. The five criteria below address the capabilities that determine whether a platform can do the job — not just whether it can be licensed and deployed.
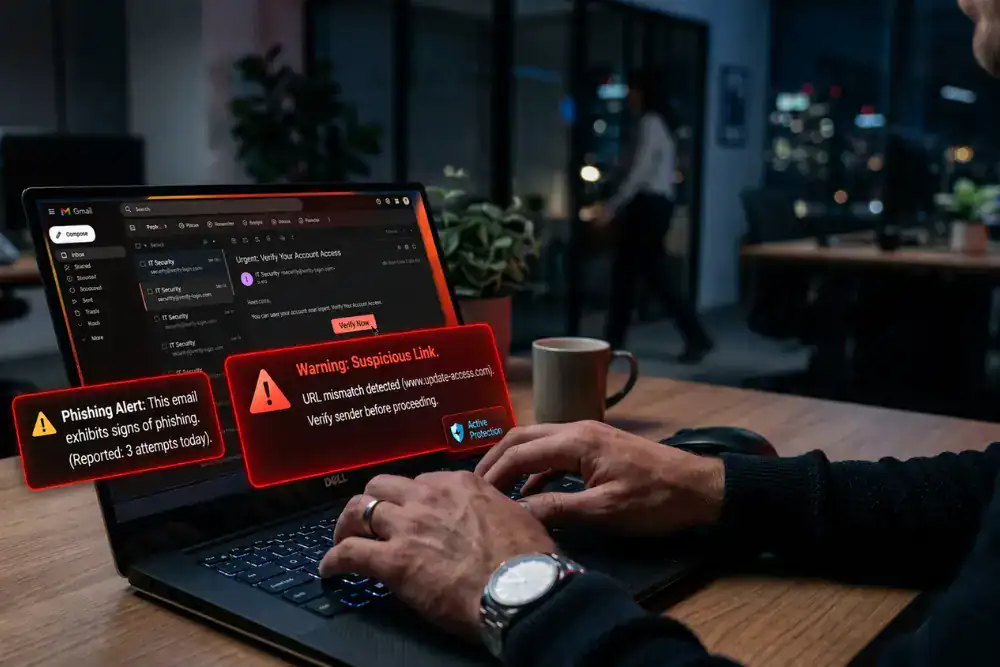
Awareness content tells people what threats look like. Phishing simulation can test how they respond to a simulated message in their inbox. Those are two different things — and simulation can be arranged separately from an awareness platform when it suits the organisation.
Where used, phishing simulation should use scenarios relevant to your sector, your organisation’s communications patterns and the attack types most likely to target your workforce. A finance team might be tested on business email compromise scenarios. An IT team might face credential-harvesting attempts.
Results should be interpreted with care: the NCSC warns that simulations can undermine trust if used punitively and cannot teach staff to spot every phishing attempt (NCSC, n.d.-b).
The threat landscape your finance director faces differs materially from the one faced by a customer service operative or a site supervisor. Effective security awareness training maps content to role-specific risk — not to job title, but to data access level, communication patterns and the specific attack vectors most likely to target that function.
Only 30 per cent of UK businesses undertook a cyber security risk assessment in the 2025/26 period (DSIT, 2026). Organisations that have not mapped their human risk profile by role may struggle to select role-appropriate training. The platform question and the risk assessment question are connected, and procurement processes that treat them separately may underperform.
If a platform uses AI to create training, ask how the content is checked for accuracy. Can managers review and approve it before staff use it? Also ask what staff or company data the AI uses and whether that data is used to train AI models.
If training adapts to each learner, ask how their role and previous results shape it. Check whether managers can change the recommendations.
The purpose of security awareness training is to change how staff behave when they encounter a threat. Assessment scores measure whether staff can identify the correct answer in a low-pressure testing environment. These are not the same thing.
A platform can help assess behaviour by tracking responses to simulated attacks over time and identifying teams that may need further support. Simulation results need to be interpreted alongside reporting and incident data. A platform that measures assessment scores tells you who completed the module with a passing mark.
Ask suppliers one simple question: what happens when someone scores 90 per cent on an assessment but repeatedly struggles with simulated phishing? If the answer is only a remedial module, ask how reporting data and feedback will inform further support. Whether anyone is actually more capable of handling a real threat is a different question — and an assessment score alone cannot answer it.
Ask to see a sample dashboard. For phishing simulations, check that it shows the percentage of staff who reported the message and the percentage who clicked its link.
Ask whether managers can compare results across teams and see how they change over time. Check that reports can be filtered by date and downloaded for review.
Under the UK GDPR, if your organisation experiences a personal data breach that meets the reporting threshold, you must notify the ICO within 72 hours of becoming aware of it, where feasible (ICO, n.d.-c). If the ICO investigates, it may ask what organisational measures were in place.
Before you sign any platform contract, ask for a sample training report. Useful fields may include the specific content completed by each staff member; the version of that content; assessment scores achieved; completion dates; and the date of the most recent content update. A pass-or-fail report alone may not meet your organisation’s evidence needs, but the ICO does not prescribe this exact list of fields (ICO, n.d.-d).
Security threats can evolve faster than annual training cycles. Tactics, techniques and procedures used by attackers change continuously. Phishing lures are updated to reference current events, trusted brands and organisation-specific contexts.
Ask whether the platform reflects current National Cyber Security Centre (NCSC) guidance, including the NCSC’s 10 Steps to Cyber Security framework, and how frequently its content is reviewed. If simulations are included, ask how often the templates are updated.
An important factor in whether a programme changes behaviour does not appear on any product sheet. A security awareness training platform is a tool. It operates within a security culture — and that culture is set by leadership behaviour, reporting norms and the organisational response to staff who report suspected incidents.
Staff who work in organisations where reporting a suspected phishing attempt is welcomed, acted on quickly and communicated back to the team are more likely to report under pressure. Staff who work in organisations where security is treated as an IT function, and reporting feels like an admission of failure, will not. No platform changes that dynamic. Leadership does.
The question to ask any platform supplier is not only what the training covers. It is how the platform is designed to be integrated into a broader security culture programme — and what evidence they can provide that organisations with similar workforce profiles have achieved measurable behaviour change, not just completion rates.
Suppliers who answer that question specifically are offering something different from the commodity end of the market. Their answers can help organisations judge whether the product fits their needs before signing.
Most organisations can tell you which platform they selected and why. Fewer can tell you who is responsible for what the platform does — or does not do — six months after it went live.
Even capable platforms fail when no one owns the programme properly. It is rarely a platform selection problem that produces the outcome.
For example, a failure can occur after the contract is signed. A platform is deployed, an IT team or compliance function is assigned administrative access, and the programme goes live. Completion rates are high in the first quarter because training has been flagged as mandatory. Phishing simulation click-through rates improve across the first two cycles because staff have learned to recognise the template scenarios. The dashboard shows green. The licence is renewed.
What the dashboard does not show is what happens when a novel spear-phishing attempt arrives — one tailored to a specific role, timed to a real operational pressure, and absent from every simulation template deployed to date. When it arrives, the programme’s actual effect on behaviour is tested. The dashboard alone may not measure it.
A platform administered by an IT team and reviewed only at licence renewal may function mainly as a compliance record-keeping system.
The mechanism is structural. IT and compliance teams may hold the platform access, generate the reports, and own the renewal decision. They may not have authority over department-level management behaviour, induction processes, or how incidents are handled when staff report them. Department behaviour, induction quality and incident response culture affect whether awareness training transfers into behaviour under pressure — so responsibility for all three needs to be clear.
The result can be visible in data nobody acts on. Simulation results may sit in a quarterly report. Recurring difficulties in specific teams may not be discussed with line managers. The scenario library may not be updated to reflect current threat tactics.
The programme runs on schedule, but its effect on behaviour remains unclear.
Closing the loop does not require a different platform. It requires a defined ownership structure — naming who is responsible for acting on simulation data, where used, between reporting periods, who holds authority to adjust deployment when role-specific patterns emerge, and who is accountable when the programme is tested by a real incident rather than a scheduled exercise. Without a defined ownership structure, the platform’s capability is unrealised regardless of what was purchased.
Bespoke programme design can help close the gap by building content, targeting and accountability around the specific threat profile and organisational conditions the workforce actually operates in.
Two gaps recur consistently across organisations that have already invested in a platform:
- Coverage that documents completion but provides limited evidence of how staff would respond to a threat
- Deployment that reaches staff without reflecting the risks associated with their roles.
Human Focus’s CPD-certified Cyber Security Awareness Training covers how attackers exploit human behaviour, phishing and vishing recognition, password and device security, and staff responsibilities for protecting information.
The course includes an online multiple-choice assessment and a completion certificate showing the learner, company, course and completion date. These records can contribute to an organisation’s evidence of training alongside other measures.
For organisations that have identified role-specific threat exposure, Human Focus’s bespoke training solution provides tools to create, deliver and manage custom e-learning based on their own materials, including systems and escalation procedures relevant to particular roles. Online awareness training cannot guarantee that staff will recognise every attack or replace technical safeguards and incident response.